A privacy policy can explain what a company intends to do with personal data.
But the application has to make it happen.
A user may be told that their information will be protected. The real test begins when that person enters their name into a form, uploads a document, creates an account, contacts customer support or withdraws consent.
- Where does that information go?
- Who can access it?
- How long does the application keep it?
- Which systems receive it?
- And when it is no longer needed, can the application actually remove it?
These are not questions that should be answered after development is complete.
They belong in the architecture.
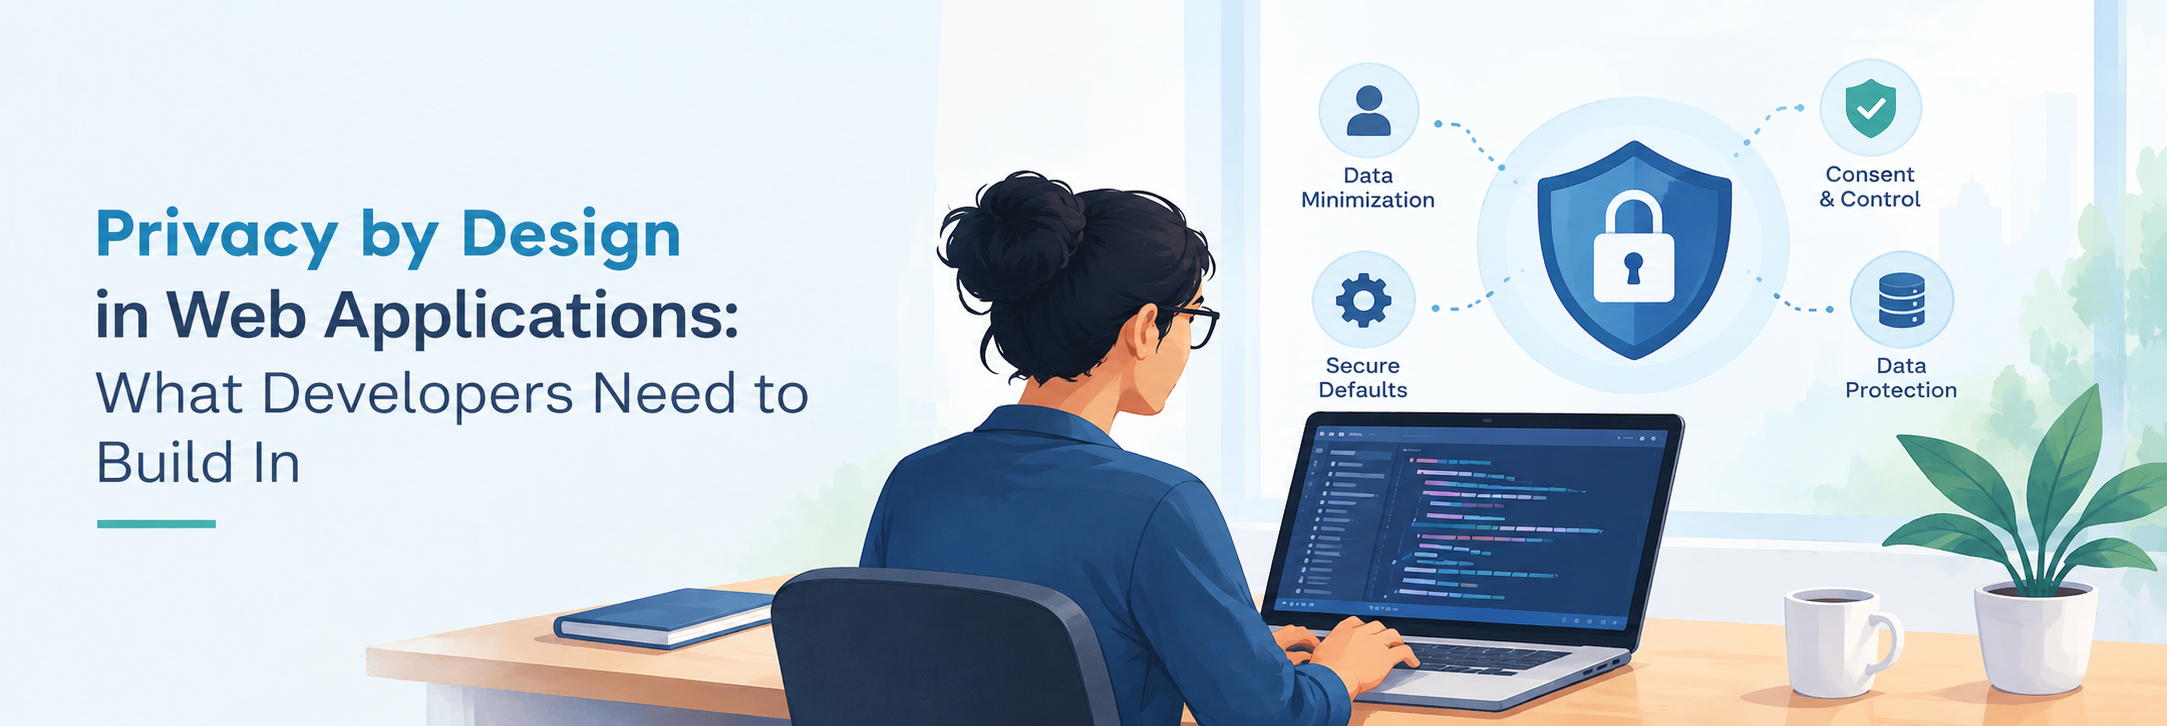
That is the practical meaning of privacy by design in software development: building privacy considerations into the way an application collects, accesses, stores, processes and deletes personal data rather than attempting to add them after the system has already been built.
Privacy by Design Starts Before the First Line of Code
Imagine two teams building the same customer portal.
The first team builds the features quickly. Customer registration, document upload, dashboards, notifications and reporting are completed. Once the application is nearly ready, someone reviews its privacy requirements.
The second team starts differently.
Before designing the database, the team maps what personal data each feature needs. Before creating APIs, it determines who should be able to access that information. Before implementing document storage, it defines retention requirements. Before deployment, it considers how information will be deleted.
Both teams may eventually produce an application with the same screens.
But the second application has privacy considerations embedded in its engineering decisions from the beginning.
That is the difference between privacy added to software and privacy designed into software.
1. Collection: Build Applications That Ask for the Right Data
Every privacy conversation begins with collection.
A registration form may ask for:
- Name
- Email address
- Mobile number
- Date of birth
- Address
- Identification details
- Employment information
- Preferences
But does the application actually need all of it?
Collecting information simply because it could become useful later creates unnecessary data exposure.
It also increases the number of fields that need to be stored, protected, accessed, retained and eventually deleted.
Privacy-aware development therefore starts with a straightforward engineering question:
What data does this feature actually need to function?
That question should influence product requirements, form design, database schemas and API payloads.
Developers can also design systems so that optional information is clearly distinguished from information genuinely required for a particular function.
The result is a smaller and more manageable data footprint.
2. Access: Not Everyone Needs to See Everything
Once data enters the application, the next question is access.
A customer-support employee may need to see a customer's contact information.
They may not need access to every document associated with that customer.
A finance employee may need billing information.
They may not need access to unrelated profile information.
An administrator may have broader permissions, but even administrative access should not automatically mean unrestricted access to every piece of personal data.
This is where application architecture matters.
Privacy by design can involve:
- Role-based access controls
- Permission-based APIs
- Authentication
- Authorisation
- Least-privilege principles
- Separation of sensitive functions
- Access logging
- Administrative controls
The objective is not simply to prevent outsiders from entering the application.
It is also to ensure that legitimate users can access only the information they need for their role.
That distinction is important because privacy risks do not exist only at the application's perimeter.
They can exist inside it too.
3. Storage: Know Where Personal Data Lives
Once personal data is collected, applications may store it in several places.
- A primary database.
- A document repository.
- A cache.
- A search index.
- Application logs.
- Analytics systems.
- Backups.
- Third-party platforms.
This creates a deceptively difficult question:
Can the development team identify where personal data actually exists?
A database diagram alone may not provide the answer.
Modern applications move information between services through APIs and background processes. A customer record entered into one application may eventually appear in several connected systems.
Privacy by design therefore requires developers to understand the application's data flows, not just its user interface.
Storage decisions should consider factors such as:
- Data classification — What information is being stored?
- Access — Which application components and users can retrieve it?
- Protection — What security controls protect the stored information?
- Location — Where is the information being processed or stored?
- Retention — How long does the application need to keep it?
- Deletion — How will it be removed when it is no longer required?
These questions are particularly important when applications integrate cloud services, SaaS platforms and third-party APIs.
4. Processing: Minimise Data as It Moves Through the System
Data does not remain stationary.
It is processed.
An application may retrieve customer information, combine it with transaction data, send selected fields to another service, generate reports or use the information to trigger an automated workflow.
Every processing step creates another opportunity to expose information unnecessarily.
Consider an API that needs a customer's name and order status.
Why should it receive the customer's complete profile?
A privacy-aware architecture aims to pass only the information required for the specific operation.
This can influence:
- API request and response design
- Internal service communication
- Data transformation
- Third-party integrations
- Analytics pipelines
- Reporting systems
- Automated workflows
It is a simple principle with significant architectural consequences:
If a component does not need the data, do not give it the data.
The same thinking can apply to logs and analytics.
Developers should be careful about accidentally placing personal information into application logs, debugging systems or monitoring platforms simply because those systems capture technical events automatically.
5. Deletion: Make the End of the Data Lifecycle Real
Deletion is one of the clearest examples of why privacy is an engineering problem.
A business may decide that certain information should no longer be retained.
But can the software actually remove it?
Suppose a customer record exists in the main database.
Deleting that record may not remove:
- Uploaded files
- Search indexes
- Cached information
- Application logs
- Analytics records
- Data replicated into another system
- Information shared with integrated services
The application therefore needs a clear understanding of its data lifecycle.
Deletion should not be treated as a single database command when the architecture involves multiple systems.
Developers may need to design:
- Deletion workflows
- Data-retention rules
- Cascading deletion logic
- Record anonymisation where appropriate
- Third-party deletion processes
- Scheduled cleanup mechanisms
- Verification and audit mechanisms
The technical approach will depend on the application's architecture and applicable requirements.
The important point is that deletion needs to be designed, tested and operationalised.
Privacy by Design Is More Than Security
Security is an essential part of privacy.
But privacy by design is broader than security alone.
A highly secure system can still collect excessive information.
- It can still give users unnecessary access.
- It can still retain data longer than required.
- It can still send too much information to third-party services.
- And it can still lack a practical way to remove information from connected systems.
Security asks an important question:
- How do we protect the data?
Privacy engineering asks additional questions:
- Why are we collecting it?
- Who needs it?
- Where does it go?
- How long should it remain?
- What happens when it is no longer needed?
That is why privacy needs to be considered across the entire application lifecycle.
What Developers Need to Build In
Privacy by design does not necessarily mean adding a massive new layer of technology.
Often, it means making better engineering decisions earlier.
1. Data-aware requirements
Identify personal data involved in each feature before development begins.
2. Purpose-driven collection
Design forms and workflows to collect information that is actually required.
3. Granular access
Use roles, permissions and application controls to limit unnecessary access.
4. Controlled data flows
Ensure APIs and integrations exchange only the information required for their specific purpose.
5. Protected storage
Apply appropriate technical safeguards to databases, files and other storage components.
6. Data lifecycle controls
Define how information is retained, archived, deleted or otherwise handled when it reaches the end of its intended lifecycle.
7. Privacy-aware testing
Test not only whether the application works, but whether personal data can be accessed, exposed or retained incorrectly.
These controls become much harder to retrofit when the underlying architecture has already been built around unrestricted data collection and access.
Privacy Should Influence the Development Lifecycle
A practical privacy-by-design approach can therefore run through the entire development process.
- Requirements: Identify the personal data involved.
- Architecture: Map where the data enters, moves, resides and leaves.
- Development: Build access, consent-related workflows, protection and lifecycle controls.
- Integration: Evaluate what information connected systems actually need.
- Testing: Test data exposure, permissions, retention and deletion scenarios.
- Deployment: Confirm that privacy-related functionality works in the production environment.
- Maintenance: Review changes, integrations and new features for their impact on existing data flows.
This is particularly important for applications that evolve continuously.
- A new CRM integration can create a new data flow.
- A new analytics tool can introduce another processing environment.
- A new feature can suddenly require additional personal information.
Privacy by design therefore cannot be a one-time architecture workshop.
It needs to remain part of software development as the product changes.
Why This Matters for Businesses and Technology Partners
For a business commissioning a web application, privacy by design changes what should be expected from a development team.
The conversation should go beyond:
“Can you build the application?”
It should also include:
“How will the application handle personal data?”
For agencies, consultants and technology providers delivering projects for their clients, the same principle applies.
You may already own the client relationship, requirements and solution strategy. But the engineering partner responsible for implementation needs to understand how privacy considerations translate into application architecture and code.
That makes privacy-aware engineering capability valuable not only to companies building their own products, but also to technology partners extending their delivery capacity.
The client may see one technology solution.
Behind it, several teams may be contributing to architecture, development, integrations and testing.
Privacy needs to survive that entire delivery chain.
The Best Time to Design Privacy Is Before You Need It
The cost of changing a data architecture increases as an application grows.
Adding a new field to a form may be simple.
Discovering years later that the same information has been replicated across multiple databases, APIs, analytics systems and third-party platforms is a very different problem.
That is why privacy by design in software development is ultimately about timing.
The earlier privacy enters the engineering conversation, the more naturally it can become part of the architecture.
Instead of asking developers to “make the application privacy compliant” at the end, businesses can build privacy considerations into the product from the beginning.
- Collect less where possible.
- Limit access.
- Understand where data lives.
- Control how it moves.
- Protect it while it is processed.
- And make deletion an actual technical capability.
That is privacy by design in practice.
Building a Privacy-Aware Web Application?
Whether you are developing a new product, modernising an existing application or delivering software for a client, Zillion IT Solutions can help translate privacy requirements into practical application engineering decisions.
From architecture and database design to APIs, integrations, access controls, testing and data lifecycle workflows, the goal is to build privacy considerations into the application rather than treating them as an afterthought.
Because privacy should not simply be documented by software teams. It should be designed into the software they build.