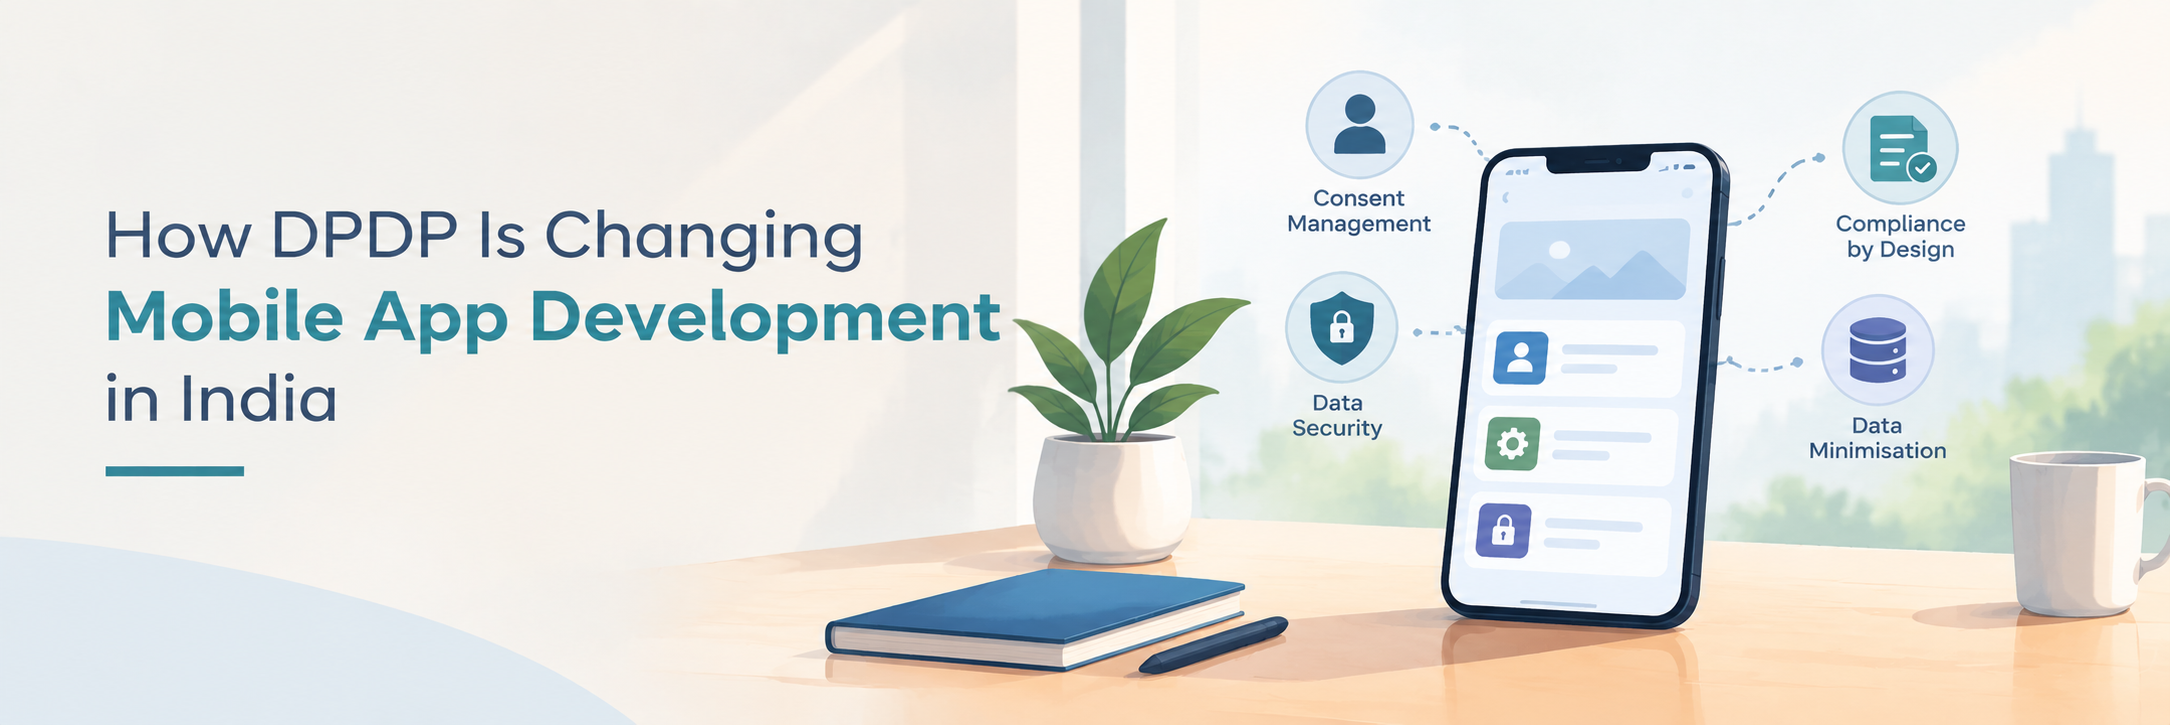
A mobile app can know where a user is, who they are, what they search for, what they buy, how they behave, which device they use and, sometimes, far more than the user realises.
That is what makes mobile applications powerful.
It is also what makes them increasingly important from a data protection perspective.
For years, mobile app development in India largely followed a familiar formula: build the experience, connect the APIs, store the required data, integrate third-party services, test the application and publish it.
DPDP changes the question.
The question is no longer simply:
“Can we build this feature?”
It increasingly becomes:
“Can we build this feature while ensuring that personal data is collected, processed, protected and managed appropriately throughout the application lifecycle?”
That is a fundamentally different engineering mindset.
India's Digital Personal Data Protection framework places responsibility on the Data Fiduciary for processing personal data and requires appropriate technical and organisational measures, reasonable security safeguards and responsible handling of personal data. The final DPDP Rules, notified in November 2025, further establish technology-oriented requirements around areas such as notice, security safeguards and user-facing mechanisms.
For mobile applications, this means privacy can no longer sit at the end of the development process.
It has to move closer to the architecture.
The Mobile App Is No Longer Just the Interface
One of the biggest mistakes businesses can make is thinking about a mobile application as a screen-based product.
The visible app is only one layer.
Behind it may be:
- Mobile application code
- Authentication services
- APIs
- Databases
- Cloud infrastructure
- Business logic
- Third-party integrations
- Customer support systems
- Analytics platforms
- Payment systems
- CRM or ERP platforms
- Internal administrative applications
- External service providers
A user may interact with one mobile app, but their personal data can move through an entire technology ecosystem.
This is where DPDP creates an important shift.
Mobile privacy engineering cannot be limited to what happens inside the Android or iOS application. Developers have to understand the complete data journey created by the application.
A mobile app therefore needs to be designed as part of a broader data-processing architecture.
That changes development decisions from the very beginning.
Privacy Starts Before the First Line of Code
Traditional application development often starts with requirements:
“What should the app do?”
Privacy-aware development adds another layer:
“What personal data does the application actually need to do it?”
This sounds simple, but it can change the architecture.
Consider a hypothetical retail application.
The business requirement may be:
“Create a personalised shopping experience.”
A development team could interpret this as a reason to collect extensive customer information.
But a privacy-aware engineering team asks different questions:
- What data is actually required?
- Which data supports the specific functionality?
- Where will the data be processed?
- Which systems need access to it?
- How long does each system need it?
- Does every component need the same information?
- Can the feature work without exposing unnecessary personal data?
The result is not necessarily a less capable application.
It can be a better-designed one.
This is the essence of bringing privacy considerations into software architecture rather than treating them as documentation added after development.
Mobile Architecture Needs a Data Perspective
Modern mobile applications are rarely self-contained.
A typical architecture might look like:
Mobile App → API Layer → Application Services → Database → External Systems
Now add personal data.
The architecture becomes a data-flow problem.
A developer needs to understand where personal data:
enters → moves → gets processed → gets stored → gets shared → gets removed or retained
That perspective can influence architectural decisions.
For example, an application may use different services for authentication, customer profiles, orders and communications.
Instead of allowing every service to access the complete user profile, the architecture can be designed around controlled data boundaries.
The customer-order service may need order information.
It may not need every attribute associated with the customer's identity.
That distinction matters.
Good privacy engineering therefore often overlaps with good software engineering:
clear boundaries, controlled interfaces, defined responsibilities and deliberate data flows.
APIs Become Privacy-Critical Components
For mobile applications, APIs are often the bridge between the user's device and the organisation's backend systems.
That makes API architecture particularly important.
An API should not automatically return everything the backend knows about a user simply because the information exists.
For example, imagine an endpoint returning a customer profile containing twenty fields when the mobile screen requires only five.
The application may function correctly.
But the architecture may be exposing more personal data than the feature requires.
Privacy-aware API design therefore considers questions such as:
- What information does this endpoint actually need to return?
- Who is authorised to receive it?
- Is the response appropriately scoped?
- Can different user roles receive different data?
- Are sensitive fields unnecessarily exposed?
- Are internal identifiers appearing in client-facing responses?
- Does the API expose data through unnecessary endpoints?
This is not simply a compliance exercise.
It is an application security and architecture discipline.
Privacy Changes the Development Lifecycle
Perhaps the biggest change is not a specific technical control.
It is when privacy enters the development process.
In a conventional workflow:
Requirement → Design → Development → Testing → Deployment
A privacy-aware workflow can introduce data considerations much earlier:
Requirement → Data Mapping → Architecture → Development → Privacy & Security Testing → Deployment → Monitoring
This does not mean developers need to become lawyers.
It means the development team needs enough understanding of the application's data processing to translate privacy requirements into technical decisions.
For product teams, this can become especially important when new features are introduced.
A feature request such as:
“Let's add personalised recommendations.”
may sound like a product decision.
Technically, it could introduce new data collection, new processing logic, new APIs, additional data stores and new third-party integrations.
The privacy impact therefore needs to be understood before the feature becomes deeply embedded in the architecture.
The Database Is Part of the Privacy Architecture
A database is not simply a place where application data is stored.
Its structure can determine how easily an organisation can control that data later.
For mobile applications, developers should think carefully about:
- Data relationships
- User identifiers
- Separation of sensitive information
- Access boundaries
- Data lifecycle
- Retention logic
- Auditability
- Data modification
- Data portability between services
The key question is not merely:
“Can we store this data?”
It is:
“Can we manage this data responsibly throughout its lifecycle?”
That becomes particularly important as applications evolve.
A product that begins with 10,000 users can eventually serve millions.
A data model that looked harmless during an MVP phase can become extremely difficult to govern once it is connected to dozens of services and years of historical data.
Privacy-aware architecture tries to avoid creating that future problem.
Privacy Engineering Is Also About Product Design
There is another important dimension that developers sometimes overlook.
Privacy is not only a backend problem.
The mobile interface determines how users understand and interact with data practices.
The final DPDP Rules require notices to be presented in clear and plain language and include information about the personal data being processed and the specified purpose or purposes.
That has implications for product design.
A privacy-aware mobile experience should not force users to navigate confusing screens simply to understand how their information is being processed.
The engineering and product teams need to work together.
The interface, backend behaviour and data-processing logic should tell the same story.
If the interface communicates one thing but the application technically does another, the problem is no longer just UX.
It becomes an architectural governance issue.
Security Cannot Be Separated From Privacy
A privacy-aware mobile application must also be a secure application.
The DPDP Act requires Data Fiduciaries to implement appropriate technical and organisational measures and take reasonable security safeguards to prevent personal data breaches.
For development teams, this reinforces the importance of security throughout the application lifecycle.
That includes thinking about:
- Authentication architecture
- Authorisation
- API security
- Secure data transmission
- Secrets management
- Secure application configuration
- Backend access controls
- Error handling
- Logging practices
- Vulnerability management
- Secure software updates
But there is an important distinction.
Security asks whether data is adequately protected.
Privacy asks whether the data should be collected, processed, accessed or retained in the first place, and whether it is being handled appropriately for its intended purpose.
A mobile application needs both.
Privacy Must Survive Application Evolution
A mobile application is never really finished.
New releases introduce new features.
Marketing teams introduce new campaigns.
Product teams introduce personalisation.
Developers replace APIs.
Businesses integrate new platforms.
Vendors change.
Cloud services evolve.
And every change can alter the application's data landscape.
This means privacy cannot be treated as a one-time development milestone.
It needs to become part of application maintenance.
A mature development process should therefore consider privacy when:
adding a feature → changing an API → integrating a service → redesigning a workflow → changing the data model → introducing AI → expanding into a new market
This is particularly relevant for businesses building applications intended to scale.
The cost of fixing a privacy problem after an architecture has become deeply interconnected can be far greater than designing the right data boundaries at the beginning.
The Developer's New Question
DPDP does not mean developers need to stop collecting personal data.
It means developers need to become more deliberate about it.
A strong mobile development team should increasingly be able to answer questions such as:
What personal data does this feature use?
Why does the feature need it?
Where does that data travel?
Which application components can access it?
Which external systems receive it?
What happens when the business no longer needs it?
Can the application enforce the intended data-handling rules technically?
These questions create a bridge between privacy requirements and software architecture.
And that bridge is where privacy engineering becomes valuable.
What DPDP Means for Mobile App Development Teams?
For businesses, the implication is straightforward.
DPDP should not be treated as something to address after the application has already been built.
For development teams, the implication is even more practical.
Privacy considerations need to become part of:
Product Requirements → Architecture → Development → Testing → Deployment → Maintenance
That does not require every developer to become a privacy specialist.
It requires the development process to recognise personal data as an architectural concern.
For technology partners and software development teams, this also creates a new expectation.
Clients increasingly need development teams that can translate privacy requirements into practical application decisions—without turning every project into a legal exercise.
That means understanding both sides:
what the regulation expects and what the technology can actually enforce.
Building Mobile Apps for a Privacy-Aware India
India's DPDP framework is changing the conversation around digital products.
The final Rules were notified in November 2025, while different provisions of the Act and Rules have phased commencement dates. This means businesses and development teams should distinguish between the framework being established and the specific provisions that are operational at a particular point in time.
For mobile application development, however, the larger lesson is already clear.
Privacy cannot remain a policy document sitting outside the product.
It has to influence the product itself.
The strongest applications of the next phase of India's digital economy will not simply be fast, intuitive and feature-rich.
They will be designed with a clear understanding of how personal data moves through the technology behind the experience.
That is the real shift DPDP brings to mobile application development.
Not simply more compliance.
Better questions at the architecture table.
And ultimately, better software.
Building a DPDP-Ready Mobile Application?
Whether you are building a new mobile product, modernising an existing application or extending your development capability for a client, privacy considerations need to be designed into the technology—not added after development.
Zillion IT Solutions brings more than two decades of software development experience to web, mobile, cloud and AI-enabled application engineering, helping businesses translate evolving technology and privacy requirements into practical software architectures.
Building or modernising a mobile application? Talk to Zillion about developing a privacy-aware, scalable application architecture designed for the realities of today's digital ecosystem.